SurfacesAvailable
Fix the finding in code and run the check.
Deixic Code is a native coding agent for the terminal, scripts, and CI. It changes the code behind a failing security finding, runs your tests before you commit, and asks you before it runs a risky command. Settings in your other systems are changed through Deixic's connections, with a receipt.
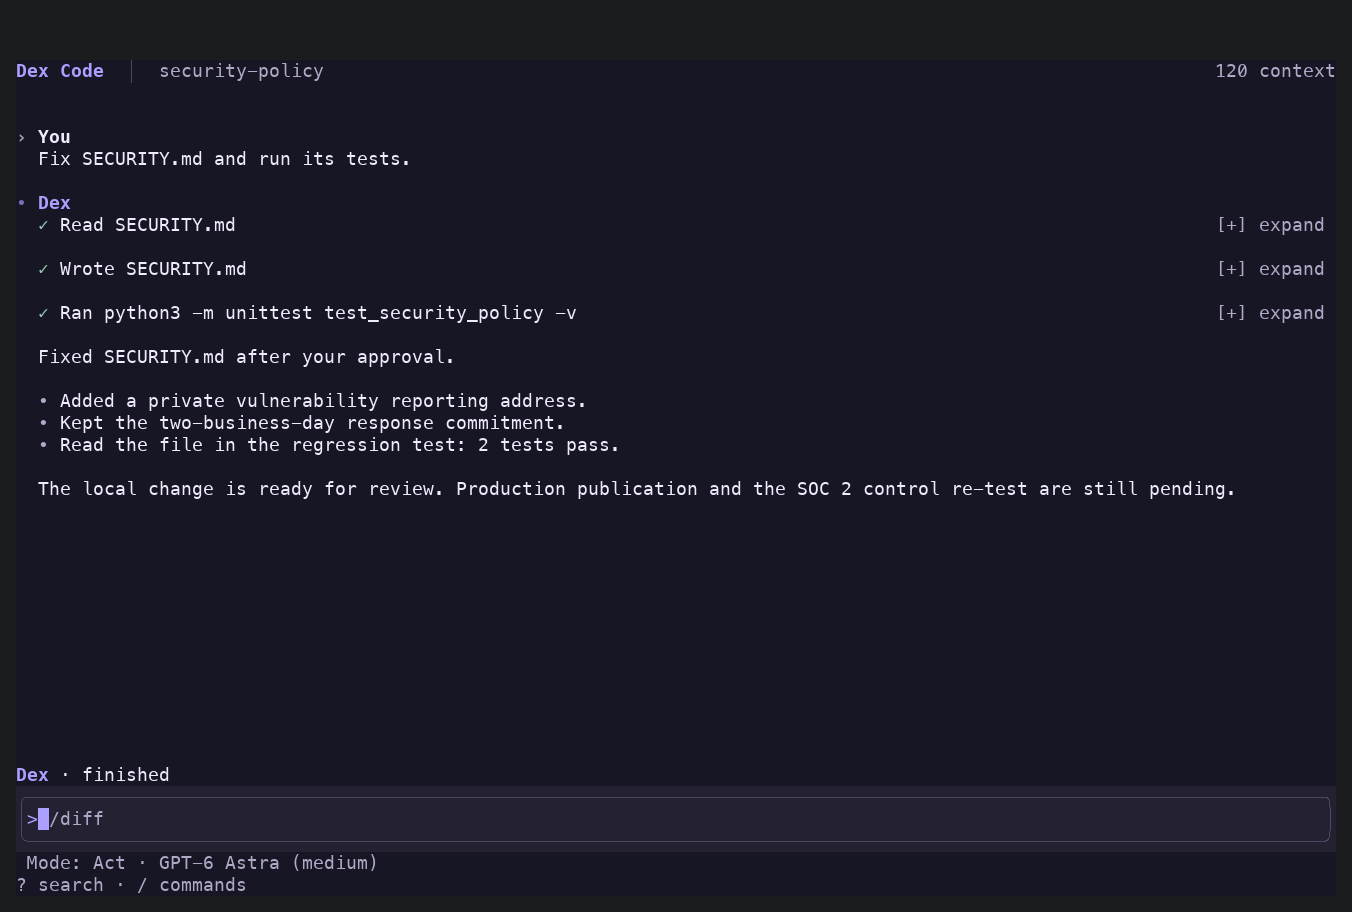
curl -fsSL https://raw.githubusercontent.com/dx-corp/code/main/scripts/install.sh | bashA code-side finding, fixed and checked.
Example terminal session with demo data.
- Finding
A scan flags a database password committed in a deploy config file.
- Change
Dex moves the value to an environment reference and removes it from the file.
- Check
Dex runs your test suite before the commit. 214 tests pass.
- Command approval
Dex asks before running a history rewrite to purge the old value. You approve or deny in the terminal.
Terminal, scripts, CI
Run it interactively, from scripts with exec, or headless in CI so the check runs on every change.
Guardrails on your machine
An action firewall and approvals gate risky commands, with an optional macOS or Linux sandbox, signed releases, and automatic updates.
Commands cannot sneak past
The firewall reads commands the way your shell does, so wrappers, quoting, and escapes do not hide a dangerous one.
A second model checks the work
Pair a primary model with a reviewer model from a different provider.
A team of agents
Split big changes across explore, plan, code, and review agents, each in its own worktree.
Undo a wrong turn
Rewind the conversation to an earlier turn and, in a Git repository, the file changes with it.
Pick up where you left off
Resume, branch, or move a session to another machine with credentials stripped out.
In your editor
Runs inside IntelliJ, PyCharm, the JetBrains family, Zed, and any editor that speaks the Agent Client Protocol.